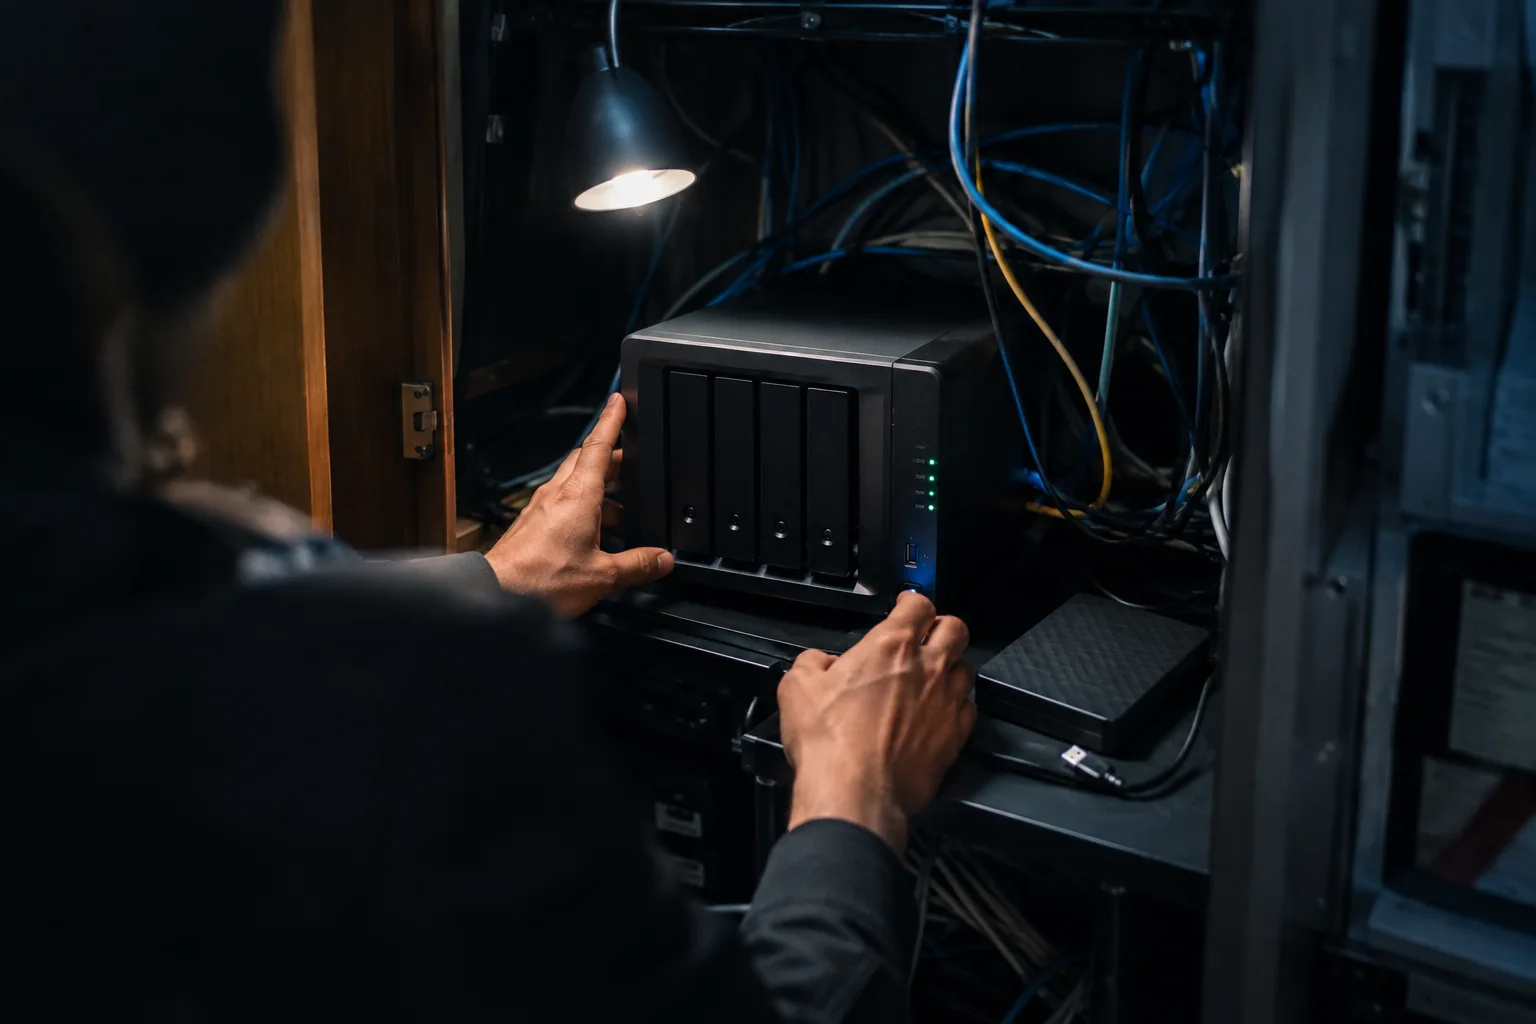
- Threat actors were exploiting a vulnerability patched in December 2024 against outdated DSM devices.
- Synology said the attacks aim to encrypt data and extort ransom.
Synology said on Oct 29, 2026, that threat actors were exploiting a vulnerability patched in December 2024 against devices running outdated versions of its DiskStation Manager operating system.
Synology said the attacks aim to encrypt data and extort ransom.
On this page
C3RB3R ransomware locks files and leaves ransom notes
The Hacker News said customers reported that C3RB3R ransomware locked files with a .L0CK3D extension. It also said the malware dropped a ransom note named read-me3.txt in each encrypted directory.
The Hacker News said C3RB3R scanned files on compromised devices while skipping 27 directories and certain extensions.
Synology lists upgrade levels for DSM branches
For DSM 7.2.2, Synology listed 7.2.2-72806-1 or above. For DSM 7.2.1, it listed 7.2.1-69057-6 or above.
| DSM branch | Upgrade level |
|---|---|
| DSM 7.2.2 | 7.2.2-72806-1 or above |
| DSM 7.2.1 | 7.2.1-69057-6 or above |
| DSM 7.2 | 7.2-64570-4 or above |
| DSM 7.1 | 7.1.1-42962-7 or above |
| DSM 6.2 | 6.2.4-25556-8 or above |
Unit 42 reported earlier NAS ransomware activity
Unit 42 said researchers found a 2021 eCh0raix variant targeting both Synology and QNAP NAS devices. Its report, published on Aug 10, 2021, said some 250,000 QNAP and Synology NAS devices were exposed to the public internet at that time.
Synology urged users running vulnerable versions to update DSM and recommended enabling automatic updates to keep the software current.
What to do now
- Update DSM immediately to protect your systems.
- Enable automatic updates to keep DSM up to date at all times.
FAQ
What happened to Synology DSM devices?
Synology said threat actors were exploiting a vulnerability patched in December 2024 against devices running outdated DSM versions.
What can the Synology attacks do?
Synology said the attacks aim to encrypt data and extort ransom.
Which Synology DSM versions have listed upgrade levels?
Synology listed upgrade levels for DSM 7.2.2, 7.2.1, 7.2, 7.1 and 6.2.
What is C3RB3R ransomware?
The Hacker News said C3RB3R ransomware locked users’ files with a .L0CK3D extension and dropped a ransom note named read-me3.txt in each encrypted directory.
Did Synology recommend automatic updates?
Yes. Synology recommended enabling automatic updates to keep DSM up to date at all times.
Sources
- New eCh0raix Ransomware Variant Targets QNAP and Synology Network-Attached Storage Devices, Unit 42Primary
- Synology urges users to update DSM following ransomware attacks on outdated DSM versionsSynology Inc., SynologyPrimary
- Synology NAS Devices Targeted in Ransomware Attacks Exploiting Patched DSM Flaw, The Hacker News
- Synology warns of C3RB3R ransomware attacks targeting NAS devices, BleepingComputer
How we checked this story
| Claim | Source | Status |
|---|---|---|
| Synology said it observed threat actors exploiting a vulnerability patched in December 2024 against devices running outdated DSM versions. | Synology, via The Hacker News | Attributed |
| Synology said the attacks aim to encrypt data and extort ransom. | Synology | Confirmed |
| BleepingComputer reported that Synology warned customers to update their devices immediately because of a surge in C3RB3r ransomware attacks. | Synology, via BleepingComputer | Attributed |
| The Hacker News said synology listed CVE-2024-10441 with a CVSS score of 9.8. | The Hacker News | Attributed |
| The Hacker News said synology listed CVE-2024-50629 with a CVSS score of 5.3. | The Hacker News | Attributed |
| The Hacker News said synology listed CVE-2024-10445 with a CVSS score of 4.3. | The Hacker News | Attributed |
| Qihoo 360 listed CVE-2026-13684 with a CVSS score of 9.8. | Qihoo 360 Internet Security Center, via The Hacker News | Attributed |
| Qihoo 360 listed CVE-2026-13639 with a CVSS score of 9.8. | Qihoo 360 Internet Security Center, via The Hacker News | Attributed |
| Synology addressed the listed issues in DSM 7.2.2-72806-1 or above. | Synology, via The Hacker News | Attributed |
| Synology addressed the listed issues in DSM 7.2.1-69057-6 or above. | Synology, via The Hacker News | Attributed |
| Synology addressed the listed issues in DSM 7.2-64570-4 or above. | Synology, via The Hacker News | Attributed |
| Synology addressed the listed issues in DSM 7.1.1-42962-7 or above. | Synology, via The Hacker News | Attributed |
| Synology addressed the listed issues in DSM 6.2.4-25556-8 or above. | Synology, via The Hacker News | Attributed |
| The Hacker News said customers reported that C3RB3R ransomware locked files with a .L0CK3D extension. | The Hacker News | Attributed |
| The Hacker News said c3RB3R drops a ransom note named read-me3.txt in each encrypted directory. | The Hacker News | Attributed |
| Unit 42 reported a 2021 eCh0raix variant targeting both Synology and QNAP NAS devices. | Unit 42 | Attributed |
| Unit 42 reported that about 250,000 QNAP and Synology NAS devices were exposed to the public internet in 2021. | Unit 42 | Attributed |
| unit42.paloaltonetworks.com published its report on Aug 10, 2021. | unit42.paloaltonetworks.com | Confirmed |
Could not verify
- Whether the attacks exploited CVE-2024-10441, CVE-2024-50629, CVE-2024-10445, CVE-2026-13684 or CVE-2026-13639 is not established
- How many Synology devices were compromised is not established
- Whether the attacks exploited a vulnerability other than those listed by Synology is not established
Related stories
 Vulns & PatchesSupermarket refrigeration systems across Europe disrupted by cyberattacks
 Vulns & PatchesWordPress Core flaw targeted after 7.1.4 release
 Vulns & PatchesTeamViewer flaw could let remote hosts crash viewer, possibly run code